Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.
Collabase supports several sign-in methods. You can mix and match — for example, enable Microsoft Entra ID for most users while keeping email/password available as a fallback.
Using Microsoft Entra ID? The guide IAM with Microsoft Entra ID takes you through sign-in and SCIM from the first setting in Entra to the first test.
This feature is part of Collabase Enterprise Edition.
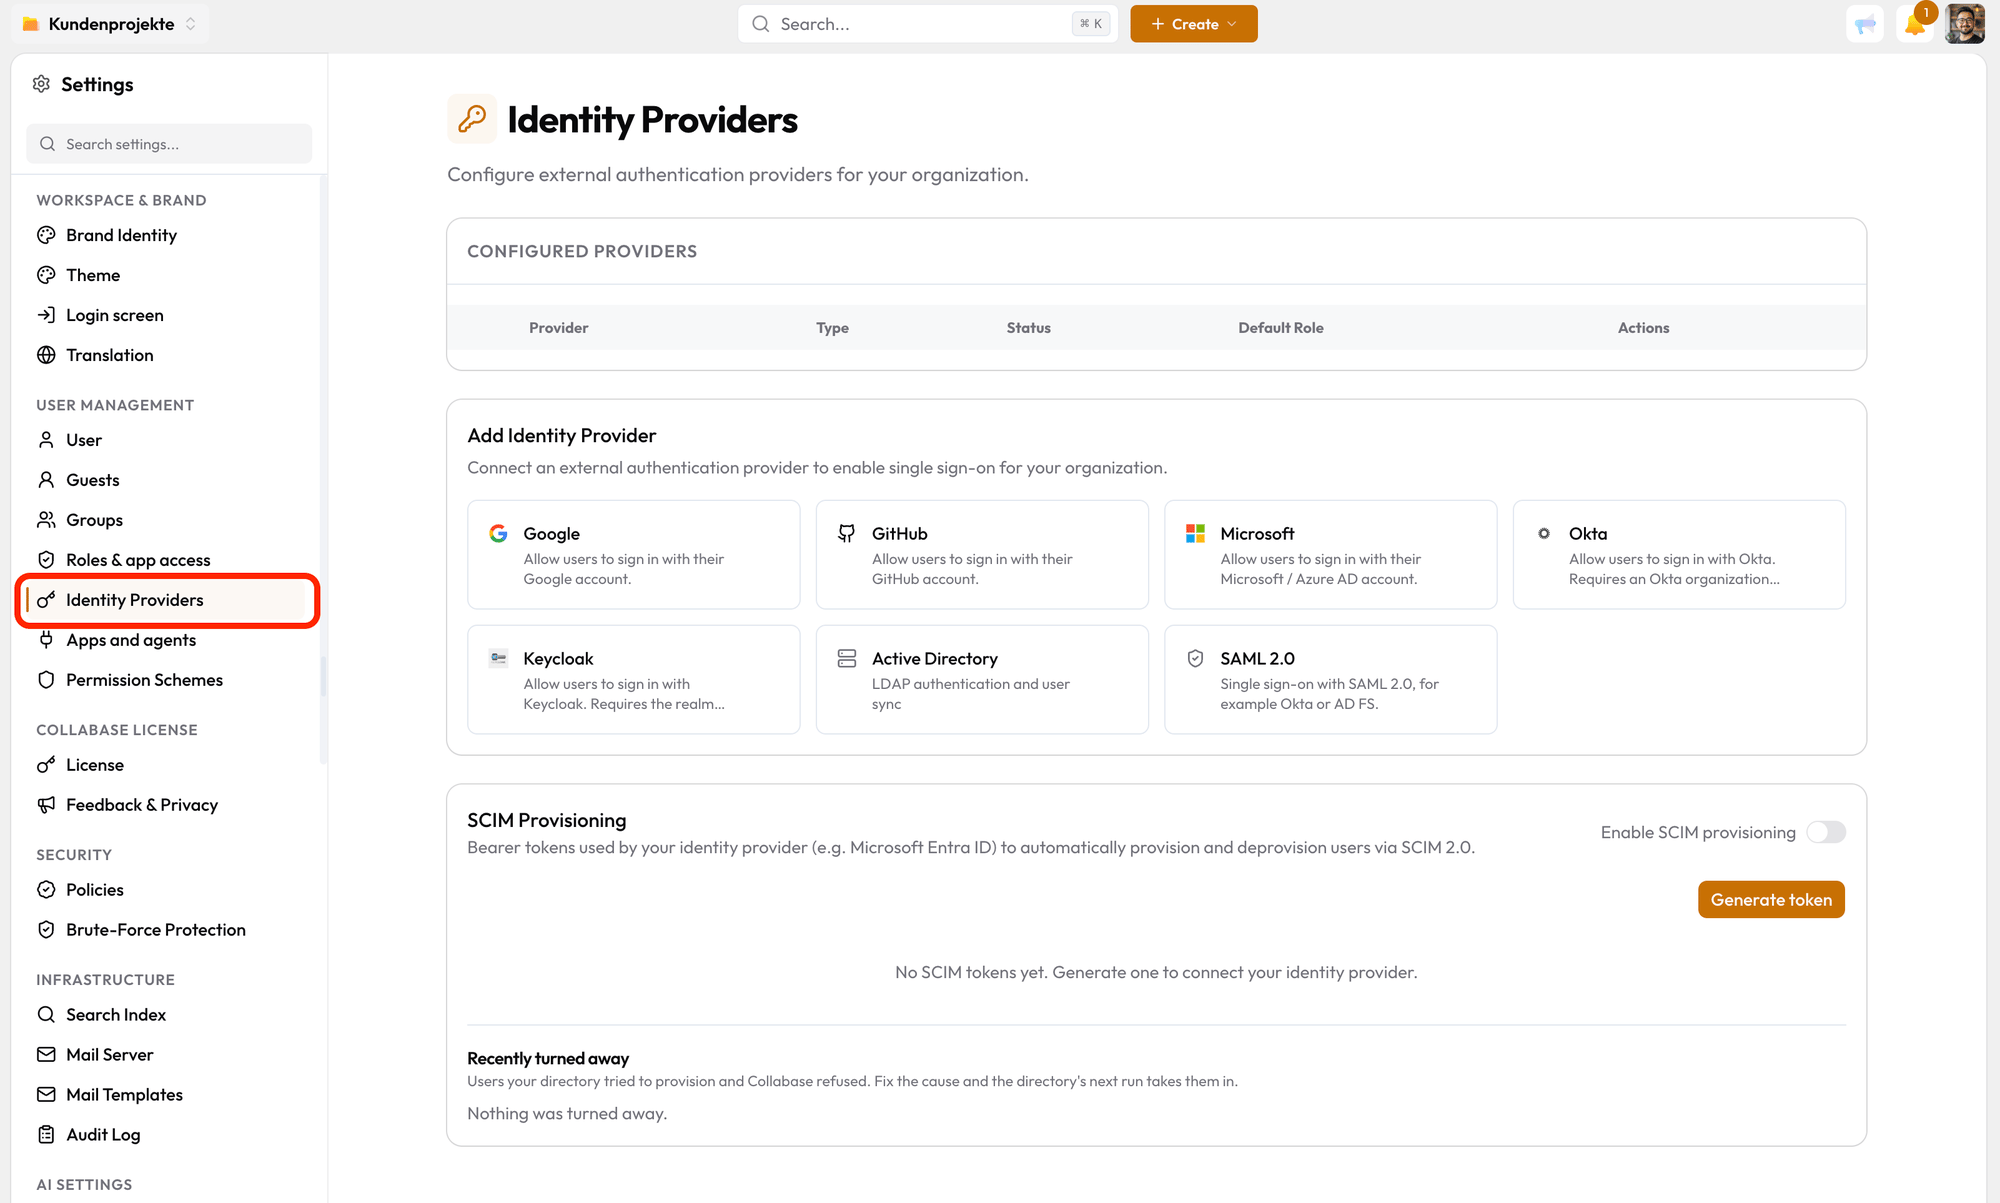
The Identity Providers page: add a provider, then connect SCIM below.
Configure identity providers under Admin → Identity Providers.
Email & Password
Always available. Users sign in with an email address and password set by an admin or chosen during registration.
OAuth 2.0
Sign in with Google, GitHub, Microsoft Entra ID, Okta, or Keycloak using an existing account. Users click a button on the login page.
SAML 2.0
Single sign-on with Okta, Microsoft Entra, or any SAML 2.0-compatible identity provider.
LDAP / Active Directory
Authenticate against your on-premises directory. Users sign in with their company credentials.
SCIM 2.0
Automated user and group provisioning from your identity provider. Accounts are created and deactivated automatically.
Email and password (always on)
Email and password authentication is always enabled and cannot be turned off. It is available at /auth/login even when other sign-in methods are active.
Keep at least one admin account using email and password. If your identity provider goes down or is misconfigured, this is how you recover access.
OAuth 2.0
OAuth lets users sign in with an existing account from another service — Google, GitHub, Microsoft Entra ID, Okta, or Keycloak. No passwords are stored in Collabase for OAuth users.
Setting up Google OAuth
1
Create an OAuth application in Google Cloud Console
Go to APIs & Services → Credentials → Create Credentials → OAuth client ID. Choose Web application as the application type.
Go to Certificates & secrets → New client secret. Copy the secret value immediately — it is not shown again.
4
Copy the Application (client) ID and Directory (tenant) ID
Both are shown on the app registration’s Overview page.
5
Open Admin → Identity Providers → Microsoft
Enter the Client ID, Client Secret, and Tenant ID (Directory ID).
6
Set the default role and enable
Choose the role for new users and toggle the provider to Enabled.
Tenant ID is required for Microsoft Entra ID. Collabase will not save a Microsoft provider without one. This deliberately prevents sign-in from Microsoft accounts outside your organization — leaving the tenant unset would allow any Microsoft account in the world to sign in. Enter the Tenant ID as the ID (a GUID such as 0b6f1a2c-…), not as a domain name; a provider with a domain name cannot be used to sign in.
Setting up Okta or Keycloak
1
Register Collabase as an application
In Okta or Keycloak, create a new OIDC application. Use:
Your provider shows these after the application is created.
3
Open Admin → Identity Providers → Okta or Keycloak
Enter the Client ID and Client Secret, plus:
Okta: your organization URL (e.g. https://mycompany.okta.com)
Keycloak: your realm issuer URL (e.g. https://keycloak.example.com/realms/myapp)
4
Set the default role and enable
Choose the role for new users and toggle the provider to Enabled.
Restricting sign-in by email domain
Every OAuth provider has an Allowed email domains field and an Auto-create new users toggle.
Setting
What it does
Allowed email domains
A comma-separated list (e.g. example.com, corp.example.com). Only accounts with an email in one of these domains can sign in with this provider. Leave blank to allow any domain.
Auto-create new users
When on (default), a new Collabase account is created automatically the first time someone signs in with this provider. When off, only people who already have a Collabase account can sign in with it.
Set Allowed email domains for every provider except perhaps GitHub. Without it, anyone with an account at that provider can sign in and, if the setting above is on, get a new Collabase account. This is especially important for Microsoft, Okta, and Keycloak, where organizations are often shared across companies.
How existing accounts are linked
When someone who already has a Collabase account signs in with a provider for the first time, Collabase links the two accounts, but only if all of the following are true:
The provider is tied to your organization: Microsoft Entra ID with a Tenant ID, Okta or Keycloak with an issuer URL, or Google with a Google Workspace domain that matches the email address. GitHub never links an existing account.
The provider does not report the email address as unverified.
If you set Allowed email domains, the domain is on the list.
Exactly one active account has that email address, and it is not a guest.
The person then receives an email telling them the account was linked, and the link is recorded in the audit log. Later sign-ins use the provider’s own account ID, so a changed email address does not create a second account. If the provider reports an address that another Collabase account already uses, Collabase keeps the stored address and records the conflict in the audit log.If one of the conditions is not met, the person sees a message on the sign-in page and no account is linked or created. They can ask an administrator, or sign in with their password.
Providers that are already set up keep working after your Enterprise license expires, so nobody is locked out. You cannot add or change providers until the license is renewed.
Credentials are stored encrypted and cannot be viewed again after saving. To update a credential, enter the new value and save — the old value is replaced.
SAML 2.0
SAML 2.0 lets users sign in with Okta, Microsoft Entra, or any SAML 2.0-compatible identity provider. Once set up, users click Sign in with SSO on the login page and are redirected to your identity provider.
The page SAML single sign-on describes every setting, the account matching and the troubleshooting in detail.
What to give your identity provider
Your identity provider needs these two values to register Collabase as a service provider:
The metadata URL. You cannot change it. After you save the provider, the expanded SAML row shows it as Service provider entity ID.
Most providers can import the full configuration by fetching the metadata URL automatically. Collabase only accepts a response that answers a sign-in it started, so sign-in always begins at Collabase; logins started from the identity provider’s own portal are refused.
What you need from your identity provider
Field
Where to find it
IdP SSO URL
The sign-on URL in your IdP’s SAML application settings
IdP Certificate
The signing certificate (PEM format)
Entity ID
The IdP’s identifier string
Configuring SAML
1
Open Admin → Identity Providers and choose SAML 2.0
Under Add an identity provider, click SAML 2.0. The panel holds the settings Collabase needs from your IdP and lists the ACS URL and metadata URL your IdP needs, as described under What to give your identity provider above.
2
Register Collabase in your identity provider
Use the ACS URL and Entity ID from the table above. Configure your IdP to send the member’s email address in an attribute named email and the display name in an attribute named displayName, and to sign the assertion. Collabase reads exactly these names and refuses an assertion that is not signed. Without an email attribute it uses the name identifier as the email address. For Microsoft Entra ID, see IAM with Microsoft Entra ID.
3
Enter the IdP SSO URL, certificate, and Entity ID in Collabase
Paste the values from your identity provider into the corresponding fields. If your provider publishes a metadata URL, enter it under Import from metadata URL and click Import: Collabase fills in the Entity ID, SSO URL, and certificate. Check the values, then continue. Only public HTTPS addresses are accepted.
4
Choose the default role
Choose the role new accounts get, and whether Collabase creates an account on a person’s first sign-in.
5
Enable and save
Toggle SAML to Enabled. Users see a Sign in with SSO button on the login page.
LDAP / Active Directory
LDAP connects Collabase to your on-premises directory (Active Directory, OpenLDAP, FreeIPA, etc.) for authentication and user provisioning. Users sign in with their existing company username and password.Navigate to Admin → Identity Providers → LDAP.
Configuration fields
Field
Description
Host
Your LDAP server address
Port
389 for standard LDAP, 636 for LDAP over TLS
Use TLS
Strongly recommended for production
Bind DN
The service account used to connect to the directory (e.g. cn=svc-collabase,ou=services,dc=example,dc=com)
Bind Password
Password for the service account
Base DN
The directory path to search for users (e.g. ou=users,dc=example,dc=com)
User Search Filter
Which objects to treat as users — default: (objectClass=person)
Email Attribute
Directory attribute that holds the user’s email address
Name Attribute
Directory attribute for the user’s display name
Default Role
Role assigned to users signing in — or synced in — for the first time. For synced users this is User, or Admin if you choose it. A setting saved earlier as Viewer now creates User accounts
The panel includes preset configurations for Active Directory ((objectClass=user), userPrincipalName, displayName) and OpenLDAP ((objectClass=inetOrgPerson), mail, cn) that fill in the common attribute mappings automatically.Click Test Connection to verify that Collabase can reach your directory before saving.
A Groups Attribute field is available for future use. Group membership is not yet synchronized from your directory — group membership must currently be managed in Collabase directly.
Directory sync
When Enable auto sync is on and a Sync Interval is set, Collabase automatically imports users from your directory on that schedule:
New users in the directory are created in Collabase.
Existing users have their name updated on each sync.
Users removed from the directory are disabled in Collabase — their content is not deleted.
A user who returns to the directory is enabled again, unless an administrator disabled that account by hand. A manual lock stays until an administrator lifts it.
The last active administrator is never disabled by a sync. If the directory no longer lists that account, it stays active and the sync result says so.
Synced users get no password from Collabase. They sign in with single sign-on, or with a password an administrator sets.
Click Sync Now to trigger a manual sync at any time, in addition to the schedule.
If a sync would disable an unusually large number of users, Collabase stops and asks you to confirm. This protects you if the directory connection is misconfigured or briefly unreachable — for example, a broken search filter that only matches a fraction of your real users. Review the warning message carefully before choosing Sync anyway; only proceed if you expect that many users to have genuinely left the directory.
Every new or re-enabled user takes one place of your licensed user limit. When no place is left, the sync skips the remaining users and reports how many it skipped. The next sync adds them once you have raised the limit or freed places.
If your Enterprise licence expires, directory sync stops: Sync Now answers with a licence error and the scheduled sync does nothing. Existing accounts and sign-in are not affected. Sync resumes as soon as the licence is renewed.
A sync that finds zero users in your directory is always stopped automatically and cannot be forced through — this is treated as a configuration problem, not a real empty directory.
SCIM 2.0 automated provisioning
SCIM (System for Cross-domain Identity Management) connects your identity provider to Collabase so user accounts — and their group memberships — are created, updated, and deactivated automatically.
The page User provisioning with SCIM lists the supported operations for accounts and groups and the troubleshooting steps.
Enabling SCIM
1
Open Admin → Identity Providers
Scroll to the SCIM Provisioning section.
2
Toggle Enable SCIM provisioning
SCIM requests are rejected until this is on, even with a valid token.
3
Click Generate token
Copy the token immediately. Collabase shows it only once. A token is valid for 365 days.
4
Configure your identity provider
In your IdP’s SCIM settings, enter:
SCIM base URL:https://your-collabase-domain/api/scim/v2
Authentication method: Bearer token
Bearer token: the token you just copied
5
Assign the Collabase application to your users and groups
In your IdP, assign the Collabase SCIM application to the users or groups that should have access. The IdP pushes those users and groups to Collabase automatically.
6
Verify provisioning
Check Admin → Users to confirm the expected users were created. The Identity column on each user row shows the account’s origin.
The SCIM token is shown only once. If you lose it, click Generate token again: the new token replaces the old one, and the old one stops working immediately. Update your identity provider with the new token before its next sync. Generate a new token before the current one reaches 365 days.
What SCIM syncs automatically
Event in your IdP
What happens in Collabase
User is assigned to the Collabase app
A new Collabase account is created
User’s name, title, or department changes
The Collabase profile is updated
User is removed from the Collabase app
The Collabase account is deactivated
User is re-assigned to the app
The account is re-activated
User is added to or removed from a group
Group membership in Collabase is updated to match
SCIM does not delete accounts — it only deactivates them. Content created by the user is preserved.
How users and groups are matched
No matching by email. If your IdP sends a user whose email address already belongs to a Collabase account that SCIM has not created, Collabase rejects the user with a conflict (HTTP 409) and records the rejection in the audit log as SCIM_USER_REJECTED. Resolve it by changing the email address of one of the two accounts, then let the IdP try again.
Matching by the IdP’s own ID. A user whose external ID is already stored on a Collabase account is linked to that account. Name and email address then follow your IdP.
Deactivation by an administrator stays. If an administrator deactivated an account in Admin → Users, a later “active” message from your IdP does not reactivate it.
No free licence seat. When the licensed user limit is reached, new users and reactivations are rejected with HTTP 403.
Users that were turned away
Below the token list, the SCIM Provisioning card shows Recently turned away: the last ten users your IdP tried to create and Collabase refused, with the reason and the time. The reason is either that the email address already belongs to another account or that no licensed seat was free. Fix the cause, and the next provisioning run of your IdP takes the user in.
Groups
Groups pushed by SCIM become Collabase groups. Their members follow your IdP, so you cannot add or remove members, rename, or delete these groups in Collabase. You can still give them access to spaces. A group with the same name as an existing Collabase group takes over that group; its members are replaced by the members from your IdP. A group can have at most 1,000 members.
Updating from an earlier version
Tokens created before this update no longer work. Open Admin → Identity Providers → SCIM Provisioning, click Generate token, enter the new token in your IdP, and restart provisioning there once (in Microsoft Entra ID: Restart provisioning). Users who already have an external ID in Collabase are linked again instead of being created twice.
SCIM stops when the Enterprise licence has expired: requests are answered with HTTP 403 until the licence is renewed.
Emergency admin access
Always keep at least one admin account that can sign in with email and password — in case your identity provider is unavailable.The email/password login page is always accessible at /auth/login, even when SSO is the default sign-in method for all other users.Accounts you exempt from enforced single sign-on (by name or through a group in the SSO bypass policy) must have a second sign-in step before you can enforce SSO. If one of them signs in with a password only, Collabase refuses to save and names the accounts. Ask them to set up an authenticator app or a passkey first.
If every admin account relies exclusively on an external provider (Google, Microsoft, SAML, LDAP) and that provider goes down or is misconfigured, you will be locked out of the admin panel. Maintain one local admin account as a recovery option.
Last modified on October 27, 2026
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Collabase","description":"Guides, administration and reference for Collabase, the collaboration platform from Switzerland: Docs, Projects, Test Management, Studio, Meetings and more.","colors":{"primary":"#0f4d38","light":"#ccfc75","dark":"#ccfc75"},"logo":{"light":"https://mintcdn.com/collabase-5ba5d338/j8uDSq0SfAexl3JI/images/logo-black.svg?fit=max\u0026auto=format\u0026n=j8uDSq0SfAexl3JI\u0026q=85\u0026s=22aa49d3e2d8036d080f1efb9ff9b531","dark":"https://mintcdn.com/collabase-5ba5d338/j8uDSq0SfAexl3JI/images/logo-white.svg?fit=max\u0026auto=format\u0026n=j8uDSq0SfAexl3JI\u0026q=85\u0026s=0487f394598030171c39de08c6f366b3"},"favicon":{"light":"https://mintcdn.com/collabase-5ba5d338/j8uDSq0SfAexl3JI/images/favicon-light.png?fit=max\u0026auto=format\u0026n=j8uDSq0SfAexl3JI\u0026q=85\u0026s=d37c20abb2f09323711170c227ce7086","dark":"https://mintcdn.com/collabase-5ba5d338/j8uDSq0SfAexl3JI/images/favicon-dark.png?fit=max\u0026auto=format\u0026n=j8uDSq0SfAexl3JI\u0026q=85\u0026s=92ae1ef55e741de8ad13e652a5519c2f"},"api":{"examples":{"prefill":true,"autogenerate":true},"url":"full","mdx":{"auth":{"method":"bearer"}}},"background":{"color":{"light":"#ffffff","dark":"#101010"}},"navbar":{"primary":{"type":"button","label":"Back to website","href":"https://collabase.ch"}},"search":{"prompt":"Search the documentation"},"seo":{"metatags":{"og:site_name":"Collabase documentation","twitter:card":"summary_large_image"},"organization":{"name":"Collabase","url":"https://collabase.ch"}},"fonts":{"heading":{"family":"Inter","weight":500},"body":{"family":"Inter","weight":400}},"icons":{"library":"lucide"},"styling":{"eyebrows":"breadcrumbs","codeblocks":"dark","latex":false},"integrations":{"ga4":{"measurementId":"G-9YS9SX848Y"},"cookies":{"key":"collabase-doku-messung","value":"erlaubt"}},"errors":{"404":{"redirect":false,"title":"Page not found","description":"This page does not exist or has moved. Search above, or [go to the documentation home](/)."}},"contextual":{"options":["copy","view","chatgpt","claude","perplexity","mcp","add-mcp","cursor","vscode"],"display":"header"},"thumbnails":{"preset":"headline","eyebrow":{"source":"tab"}},"interaction":{"drilldown":true},"metadata":{"timestamp":true},"markdown":{"schema":true,"instructions":["Collabase documentation. Interface labels are quoted in English, as they appear in the product.","Features marked Enterprise need the Collabase Enterprise Edition licence."]},"navigation":{"languages":[{"language":"en","footer":{"links":[{"header":"Collabase","items":[{"label":"Website","href":"https://collabase.ch"},{"label":"Download","href":"https://collabase.ch/en/download"},{"label":"Trust center","href":"https://collabase.ch/vertrauen"},{"label":"Support","href":"https://infometis.atlassian.net/servicedesk/customer/portal/1/group/81"}]}]},"navbar":{"primary":{"type":"button","label":"Back to website","href":"https://collabase.ch"}},"href":""},{"language":"de","banner":{"content":"Die Leitfäden gibt es auf Deutsch. Die App-Referenz und die Administration liegen nur auf Englisch vor.","dismissible":true},"footer":{"links":[{"header":"Collabase","items":[{"label":"Website","href":"https://collabase.ch"},{"label":"Download","href":"https://collabase.ch/download"},{"label":"Trust Center","href":"https://collabase.ch/vertrauen"},{"label":"Support","href":"https://infometis.atlassian.net/servicedesk/customer/portal/1/group/81"}]}]},"navbar":{"primary":{"type":"button","label":"Zur Website","href":"https://collabase.ch"}},"href":"de"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"collabase-5ba5d338","hasAudioNarration":false,"actualSubdomain":"collabase-5ba5d338","customDomains":["collabase.ch"],"gitSource":{"type":"github","owner":"collabase","repo":"docs","deployBranch":"main","contentDirectory":"","isPrivate":false,"mountPath":"","label":""},"feedback":{"thumbs":true,"edits":false,"issues":false},"entitlements":{"AI_CHAT":{"status":"DISABLED"}},"buildId":"6af708e32856bcaabf05c818","clientVersion":"0.0.4177","searchFilterCounts":[{"language":"default","tag":"Apps","count":208},{"language":"default","tag":"API reference","count":128},{"language":"default","tag":"Studio","count":76},{"language":"default","tag":"Meetings","count":52},{"language":"default","tag":"CRM","count":43},{"language":"default","tag":"Administration","count":39},{"language":"en","tag":"Guides","count":29},{"language":"de","tag":"Leitfäden","count":29},{"language":"default","tag":"Guides","count":25},{"language":"default","tag":"Core concepts","count":23},{"language":"default","tag":"Projects","count":21},{"language":"default","tag":"Developers","count":18},{"language":"en","tag":"HERMES project management","count":14},{"language":"de","tag":"HERMES Projektmanagement","count":14},{"language":"en","tag":"Getting started guide","count":11},{"language":"de","tag":"Erste Schritte","count":11},{"language":"en","tag":"Release notes","count":5},{"language":"en","tag":"Releases","count":5},{"language":"de","tag":"Release Notes","count":5},{"language":"de","tag":"Versionen","count":5},{"language":"en","tag":"Collabase 1","count":4},{"language":"de","tag":"Collabase 1","count":4},{"language":"en","tag":"Welcome","count":3},{"language":"en","tag":"Administration","count":3},{"language":"de","tag":"Willkommen","count":3},{"language":"de","tag":"Administration","count":3},{"language":"en","tag":"Install and run","count":2},{"language":"de","tag":"Installieren und betreiben","count":2},{"language":"en","tag":"IAM with Microsoft","count":1},{"language":"de","tag":"IAM mit Microsoft","count":1}],"searchSettings":{"maxResults":6,"showContentSnippets":true}},"assistantConfig":{"enableAskAiButton":false,"enableStarterQuestions":false,"enableContextualStarterQuestions":false,"enableAskAiSearchBar":true},"basePath":"/docs","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-rbac-roles","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-metadata","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-serve","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"live-agents","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"starter-pricing","enabled":true,"variant":{"name":"control","enabled":true,"payload":{"type":"string","value":"control"},"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"privacy":{"consentBanner":{"enabled":true}},"googleFontsInlined":false},"customCss":[{"filePath":"style.css","content":"/* cyrillic-ext */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx3cwhsk.woff2) format('woff2');\n unicode-range: U+0460-052F, U+1C80-1C8A, U+20B4, U+2DE0-2DFF, U+A640-A69F, U+FE2E-FE2F;\n}\n/* cyrillic */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxTcwhsk.woff2) format('woff2');\n unicode-range: U+0301, U+0400-045F, U+0490-0491, U+04B0-04B1, U+2116;\n}\n/* greek */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxPcwhsk.woff2) format('woff2');\n unicode-range: U+0370-0377, U+037A-037F, U+0384-038A, U+038C, U+038E-03A1, U+03A3-03FF;\n}\n/* vietnamese */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx_cwhsk.woff2) format('woff2');\n unicode-range: U+0102-0103, U+0110-0111, U+0128-0129, U+0168-0169, U+01A0-01A1, U+01AF-01B0, U+0300-0301, U+0303-0304, U+0308-0309, U+0323, U+0329, U+1EA0-1EF9, U+20AB;\n}\n/* latin-ext */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx7cwhsk.woff2) format('woff2');\n unicode-range: U+0100-02BA, U+02BD-02C5, U+02C7-02CC, U+02CE-02D7, U+02DD-02FF, U+0304, U+0308, U+0329, U+1D00-1DBF, U+1E00-1E9F, U+1EF2-1EFF, U+2020, U+20A0-20AB, U+20AD-20C4, U+2113, U+2C60-2C7F, U+A720-A7FF;\n}\n/* latin */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 400;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxDcwg.woff2) format('woff2');\n unicode-range: U+0000-00FF, U+0131, U+0152-0153, U+02BB-02BC, U+02C6, U+02DA, U+02DC, U+0304, U+0308, U+0329, U+2000-206F, U+20AC, U+2122, U+2191, U+2193, U+2212, U+2215, U+FEFF, U+FFFD;\n}\n/* cyrillic-ext */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx3cwhsk.woff2) format('woff2');\n unicode-range: U+0460-052F, U+1C80-1C8A, U+20B4, U+2DE0-2DFF, U+A640-A69F, U+FE2E-FE2F;\n}\n/* cyrillic */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxTcwhsk.woff2) format('woff2');\n unicode-range: U+0301, U+0400-045F, U+0490-0491, U+04B0-04B1, U+2116;\n}\n/* greek */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxPcwhsk.woff2) format('woff2');\n unicode-range: U+0370-0377, U+037A-037F, U+0384-038A, U+038C, U+038E-03A1, U+03A3-03FF;\n}\n/* vietnamese */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx_cwhsk.woff2) format('woff2');\n unicode-range: U+0102-0103, U+0110-0111, U+0128-0129, U+0168-0169, U+01A0-01A1, U+01AF-01B0, U+0300-0301, U+0303-0304, U+0308-0309, U+0323, U+0329, U+1EA0-1EF9, U+20AB;\n}\n/* latin-ext */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPx7cwhsk.woff2) format('woff2');\n unicode-range: U+0100-02BA, U+02BD-02C5, U+02C7-02CC, U+02CE-02D7, U+02DD-02FF, U+0304, U+0308, U+0329, U+1D00-1DBF, U+1E00-1E9F, U+1EF2-1EFF, U+2020, U+20A0-20AB, U+20AD-20C4, U+2113, U+2C60-2C7F, U+A720-A7FF;\n}\n/* latin */\n@font-face {\n font-family: 'JetBrains Mono';\n font-style: normal;\n font-weight: 500;\n font-display: swap;\n src: url(/docs/_mintlify/assets/fonts/google/s/jetbrainsmono/v24/tDbv2o-flEEny0FZhsfKu5WU4zr3E_BX0PnT8RD8yKwBNntkaToggR7BYRbKPxDcwg.woff2) format('woff2');\n unicode-range: U+0000-00FF, U+0131, U+0152-0153, U+02BB-02BC, U+02C6, U+02DA, U+02DC, U+0304, U+0308, U+0329, U+2000-206F, U+20AC, U+2122, U+2191, U+2193, U+2212, U+2215, U+FEFF, U+FFFD;\n}\n:root{--ds-bg: #ffffff;--ds-bg-2: #fafafb;--ds-bg-3: #f3f4f6;--ds-bg-4: #edeff3;--ds-linie: #eceef2;--ds-linie-2: #e1e4ea;--ds-linie-3: #cad0d9;--ds-punkt: #b5bdc9;--ds-text-1: #17181a;--ds-text-2: #3a3f47;--ds-text-3: #6b7482;--ds-text-4: #8f99a8;--ds-signal: #10a874;--ds-signal-weich: rgb(16 168 116 / 0.12);--ds-akzent-text: #0f4d38;--ds-knopf: #ccfc75;--ds-knopf-schrift: #101010;--ds-kopf: rgb(255 255 255 / 0.9);--ds-bild-kante: rgb(0 0 0 / 0.08);--ds-hero-licht: radial-gradient(60% 70% at 50% 100%, rgb(229 233 240 / 0.9), transparent 70%);--ds-band: #101010;--ds-band-2: #17181a;--ds-band-linie-2: #2e3238}.dark{--ds-bg: #101010;--ds-bg-2: #161718;--ds-bg-3: #1c1d1f;--ds-bg-4: #232529;--ds-linie: #1f2023;--ds-linie-2: #2a2d32;--ds-linie-3: #383e47;--ds-punkt: #505967;--ds-text-1: #f3f4f6;--ds-text-2: #cad0d9;--ds-text-3: #8f99a8;--ds-text-4: #6f7988;--ds-signal: #1ae299;--ds-signal-weich: rgb(26 226 153 / 0.14);--ds-akzent-text: #ccfc75;--ds-kopf: rgb(16 16 16 / 0.88);--ds-bild-kante: rgb(255 255 255 / 0.1);--ds-hero-licht: radial-gradient(60% 70% at 50% 100%, rgb(56 62 71 / 0.35), transparent 70%);--ds-band: #0a0a0a;--ds-band-2: #131415}.brand-marker,.brand-marker-action{background:var(--ds-knopf);border-radius:0.375rem;box-decoration-break:clone;-webkit-box-decoration-break:clone;color:var(--ds-knopf-schrift);padding:0 0.3em}.dark .brand-marker,.dark .brand-marker-action{background:transparent;color:var(--ds-akzent-text);padding:0}.brand-cards [data-component-part=\"card-icon\"] svg{background-color:var(--ds-text-2)!important}.nav-tag-pill .nav-tag-pill-text{background:var(--ds-bg-3);box-shadow:inset 0 0 0 1px var(--ds-linie-2);color:var(--ds-akzent-text)}#topbar-cta-button,#topbar-cta-button a,#topbar-cta-button span{color:var(--ds-knopf-schrift)!important}html[data-current-path=\"/\"] header#navbar,html[data-current-path=\"/de\"] header#navbar{backdrop-filter:blur(12px);background-color:var(--ds-kopf)}[data-badge][data-color=\"green\"]{background:var(--ds-signal-weich);border-color:transparent;color:var(--ds-akzent-text)}h1,h2,h3{letter-spacing:-0.03em}body{letter-spacing:-0.01em}code,kbd,pre{font-family:\"JetBrains Mono\", ui-monospace, SFMono-Regular, Menlo, monospace;letter-spacing:0}.callout{box-shadow:none}.code-block{background:var(--ds-band-2);border-color:var(--ds-band-linie-2);box-shadow:none}.prose img:not([noZoom]){border:1px solid var(--ds-bild-kante);border-radius:0.75rem}.home-hero{overflow:hidden;position:relative}.home-title{color:var(--ds-text-1);font-size:2.5rem;font-weight:500;letter-spacing:-0.03em;line-height:1.05}@media (min-width: 1024px){.home-title{font-size:3.5rem}}.home-pill{color:var(--ds-text-3);display:inline-block;font-size:0.75rem;font-weight:500;letter-spacing:0.06em;text-transform:uppercase}.home-pill::before{content:\"[ \"}.home-pill::after{content:\" ]\"}.home-section-title{color:var(--ds-text-1);font-size:1.5rem;font-weight:500;letter-spacing:-0.025em}.home-link:hover{color:var(--ds-akzent-text)}.home-search,.home-cards .card{background:var(--ds-bg);border:1px solid var(--ds-linie-2);border-radius:0.75rem;box-shadow:none}.home-search{border-radius:0.625rem;width:100%}.home-cards .card:hover{background:var(--ds-bg-2);border-color:var(--ds-linie-3)}.home-cards [data-component-part=\"card-icon\"]{background:transparent}.home-cards{--home-gap: 1.25rem}[data-component-part=\"card-title\"]{letter-spacing:-0.01em}html body #banner{background:var(--ds-knopf)}html body #banner,html body #banner *{color:var(--ds-knopf-schrift)!important}.home-bg{inset:0;pointer-events:none;position:absolute}.home-bg::before{background:radial-gradient(ellipse 60% 75% at 50% 35%, var(--ds-bg-3), transparent 75%);content:\"\";inset:0;mask-image:linear-gradient(to bottom, #000 50%, transparent 100%);-webkit-mask-image:linear-gradient(to bottom, #000 50%, transparent 100%);position:absolute}.home-dots{background-image:radial-gradient(var(--ds-punkt) 1px, transparent 1.5px);background-size:22px 22px;inset:0;mask-image:radial-gradient(70% 90% at 50% 0%, #000 30%, transparent 100%);-webkit-mask-image:radial-gradient(70% 90% at 50% 0%, #000 30%, transparent 100%);opacity:0.6;position:absolute}.home-float{--r: 0deg;animation:home-float 9s ease-in-out infinite;display:none;position:absolute;transform:rotate(var(--r))}.home-float img{border-radius:1.1rem;height:4.5rem;margin:0;width:4.5rem}@media (min-width: 1100px){.home-float{display:block}}.home-float:nth-child(2){--r: -8deg;animation-delay:0s;left:6%;top:3rem}.home-float:nth-child(3){--r: 6deg;animation-delay:-2s;left:15%;top:11rem}.home-float:nth-child(4){--r: -4deg;animation-delay:-4s;left:4%;top:18rem}.home-float:nth-child(5){--r: 8deg;animation-delay:-1s;right:6%;top:4rem}.home-float:nth-child(6){--r: -6deg;animation-delay:-3s;right:15%;top:12rem}.home-float:nth-child(7){--r: 5deg;animation-delay:-5s;right:4%;top:19rem}.home-float:nth-child(8){--r: -3deg;animation-delay:-6s;left:14%;top:24rem}@keyframes home-float{0%,100%{transform:translateY(0) rotate(var(--r))}50%{transform:translateY(-10px) rotate(calc(var(--r) + 2deg))}}@media (prefers-reduced-motion: reduce){.home-float{animation:none}}.dev-hero{background:var(--ds-bg);color:var(--ds-text-2);overflow:hidden;position:relative}.dev-hero .home-title{color:var(--ds-text-1)}.dev-raster{background-image:linear-gradient(to right, var(--ds-linie) 1px, transparent 1px),\n linear-gradient(to bottom, var(--ds-linie) 1px, transparent 1px);background-position:-1px -1px;background-size:48px 48px;inset:0;mask-image:radial-gradient(ellipse 80% 70% at 50% 45%, #000 30%, transparent 100%);-webkit-mask-image:radial-gradient(ellipse 80% 70% at 50% 45%, #000 30%, transparent 100%);pointer-events:none;position:absolute}.dev-hero-inner{align-items:center;display:grid;gap:3rem;margin:0 auto;max-width:72rem;padding:4rem 1.5rem;position:relative}@media (min-width: 1024px){.dev-hero-inner{grid-template-columns:minmax(0, 7fr) minmax(0, 5fr);padding:6rem 2.5rem}}.dev-hero-mark{display:flex;justify-content:center}@media (min-width: 1024px){.dev-hero-mark{justify-content:flex-end}}.dev-mark{height:auto;max-width:22rem;width:100%}.dev-mark *{vector-effect:non-scaling-stroke}.dev-mark .dz-linie,.dev-mark .dz-signal{fill:none;stroke-linecap:round;stroke-linejoin:round;stroke-width:1.5}.dev-mark .dz-linie{stroke:var(--ds-punkt)}.dev-mark .dz-signal{stroke:var(--ds-signal)}.dev-mark .dz-hilfe{fill:none;stroke:var(--ds-linie-3);stroke-dasharray:2 4;stroke-linecap:round;stroke-width:1}.dev-mark .dz-punkt{fill:var(--ds-punkt)}@keyframes dev-schleife{0%{stroke-dashoffset:100;opacity:1}38%{stroke-dashoffset:0;opacity:1}78%{stroke-dashoffset:0;opacity:1}94%{stroke-dashoffset:0;opacity:0}100%{stroke-dashoffset:100;opacity:0}}.dev-mark .dev-schleife{animation:dev-schleife 9s cubic-bezier(0.45, 0, 0.25, 1) infinite;stroke-dasharray:100;stroke-dashoffset:100;stroke-width:0.45;vector-effect:none}.dev-mark .dev-schleife-spaet{animation-delay:0.7s;animation-fill-mode:backwards}@media (prefers-reduced-motion: reduce){.dev-mark .dev-schleife{animation:none;opacity:1;stroke-dashoffset:0}}#table-of-contents nav{position:relative}#table-of-contents-content{padding-left:1rem}#table-of-contents [data-layout-item=\"toc-item\"][data-active]>[data-layout-item=\"toc-item-link\"]{color:var(--ds-akzent-text)!important;font-weight:500}#table-of-contents [data-layout-item=\"toc-indicator\"]{background-color:var(--ds-akzent-text);border-radius:9999px;height:0.375rem;left:0;opacity:0;position:absolute;top:0;transform:translateY(-50%);transition:top 0.16s cubic-bezier(0.25, 0.75, 0.2, 1), opacity 0.16s;width:0.375rem}@media (prefers-reduced-motion: reduce){#table-of-contents [data-layout-item=\"toc-indicator\"]{transition:none}}.dev-tiles{display:grid;gap:2.5rem 1.5rem;grid-template-columns:1fr}@media (min-width: 640px){.dev-tiles{grid-template-columns:repeat(2, minmax(0, 1fr))}}.dev-tile{border-bottom:0!important;color:inherit;display:block;text-decoration:none!important}.dev-tile-bild{align-items:center;aspect-ratio:16 / 9;background-color:var(--ds-bg-2);background-image:linear-gradient(to right, var(--ds-linie) 1px, transparent 1px),\n linear-gradient(to bottom, var(--ds-linie) 1px, transparent 1px);background-position:-1px -1px;background-size:24px 24px;border:1px solid var(--ds-linie-2);border-radius:1rem;display:flex;justify-content:center;transition:border-color 0.12s ease}.dev-tile:hover .dev-tile-bild{border-color:var(--ds-linie-3)}.dev-tile-svg{height:auto;margin:0;max-width:62%;width:100%}.dev-tile-titel{align-items:center;color:var(--ds-text-1);display:flex;font-weight:500;gap:0.5rem;margin:1rem 0 0.25rem}.dev-tile-text{color:var(--ds-text-3);margin:0}.dev-tile-svg .dz-linie,.dev-tile-svg .dz-signal{fill:none;stroke-linecap:round;stroke-linejoin:round;stroke-width:1.5}.dev-tile-svg .dz-linie{stroke:var(--ds-punkt)}.dev-tile-svg .dz-signal{stroke:var(--ds-signal)}.dev-tile-svg .dz-hilfe{fill:none;stroke:var(--ds-linie-3);stroke-dasharray:2 4;stroke-linecap:round;stroke-width:1}.dev-tile-svg .dz-flaeche{fill:var(--ds-bg-3);stroke:var(--ds-linie-3);stroke-width:1}.dev-tile-svg .dz-tief{fill:var(--ds-bg);stroke:var(--ds-linie-3);stroke-width:1}.dev-tile-svg .dz-balken{fill:var(--ds-linie-3)}.dev-tile-svg .dz-punkt{fill:var(--ds-punkt)}.dev-tile-svg .dz-signal-f{fill:var(--ds-signal)}.dev-tile-svg .dz-signal-weich{fill:var(--ds-signal-weich);stroke:var(--ds-signal);stroke-width:1}.dev-tile-svg .dz-text{fill:var(--ds-text-3);font-family:Inter, system-ui, sans-serif;font-size:8px;font-weight:500;letter-spacing:0}.dev-tile-svg .dz-text-hell{fill:var(--ds-text-1)}.dev-tile-svg .dz-code{font-family:\"JetBrains Mono\", ui-monospace, monospace}"}],"page":{"pagePath":"admin/identity-providers","slug":"/admin/identity-providers","pageMetadata":{"title":"Identity providers","sidebarTitle":"Identity Providers","description":"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.","icon":"fingerprint","href":"/admin/identity-providers"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,hr:`hr`,li:`li`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Card,CardGroup,CodeBlock,Frame,Heading,Info,Note,OptimizedImage,Step,Steps,Table,Tip,Warning}=_components;if(!Card)_missingMdxReference(`Card`,true);if(!CardGroup)_missingMdxReference(`CardGroup`,true);if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!Note)_missingMdxReference(`Note`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Tip)_missingMdxReference(`Tip`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsx(_components.p,{children:`Collabase supports several sign-in methods. You can mix and match — for example, enable Microsoft Entra ID for most users while keeping email/password available as a fallback.`}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`Using Microsoft Entra ID? The guide `,_jsx(_components.a,{href:`/admin/iam-microsoft-entra`,children:`IAM with Microsoft Entra ID`}),` takes you through sign-in and SCIM from the first setting in Entra to the first test.`]})}),`\n`,_jsx(Info,{children:_jsx(_components.p,{children:`This feature is part of Collabase Enterprise Edition.`})}),`\n`,_jsx(Frame,{caption:`The Identity Providers page: add a provider, then connect SCIM below.`,children:_jsx(OptimizedImage,{src:`https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=acedc222a458a32a741d23b121b2e96e`,alt:`The Identity Providers page with the providers you can add and the SCIM Provisioning card`,\"data-og-width\":`2000`,width:`2000`,\"data-og-height\":`1203`,height:`1203`,\"data-path\":`images/iam-identity-providers.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=280\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=254ef43eef27afe0e55a82206dad1620 280w, https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=560\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=75cc8fdf342ab0a0769059cf231141e8 560w, https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=840\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=e5e35a701f3e5e6697bf71cfa75db5c3 840w, https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=1100\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=b239e6aa2aeff24dcc7997376bfb84ed 1100w, https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=1650\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=ea099f82a52b6013e5ee49869194c1d9 1650w, https://mintcdn.com/collabase-5ba5d338/bgJOtpx5plU9bgSv/images/iam-identity-providers.png?w=2500\u0026fit=max\u0026auto=format\u0026n=bgJOtpx5plU9bgSv\u0026q=85\u0026s=642e5ecf865d86dd9ceb5609b41684bb 2500w`})}),`\n`,_jsxs(_components.p,{children:[`Configure identity providers under `,_jsx(_components.strong,{children:`Admin → Identity Providers`}),`.`]}),`\n`,_jsxs(CardGroup,{cols:3,children:[_jsx(Card,{title:`Email \u0026 Password`,icon:`lock`,children:_jsx(_components.p,{children:`Always available. Users sign in with an email address and password set by an admin or chosen during registration.`})}),_jsx(Card,{title:`OAuth 2.0`,icon:`key`,children:_jsx(_components.p,{children:`Sign in with Google, GitHub, Microsoft Entra ID, Okta, or Keycloak using an existing account. Users click a button on the login page.`})}),_jsx(Card,{title:`SAML 2.0`,icon:`shield`,children:_jsx(_components.p,{children:`Single sign-on with Okta, Microsoft Entra, or any SAML 2.0-compatible identity provider.`})}),_jsx(Card,{title:`LDAP / Active Directory`,icon:`server`,children:_jsx(_components.p,{children:`Authenticate against your on-premises directory. Users sign in with their company credentials.`})}),_jsx(Card,{title:`SCIM 2.0`,icon:`users`,children:_jsx(_components.p,{children:`Automated user and group provisioning from your identity provider. Accounts are created and deactivated automatically.`})})]}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`email-and-password-always-on`,children:`Email and password (always on)`}),`\n`,_jsxs(_components.p,{children:[`Email and password authentication is always enabled and cannot be turned off. It is available at `,_jsx(_components.code,{children:`/auth/login`}),` even when other sign-in methods are active.`]}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`Keep at least one admin account using email and password. If your identity provider goes down or is misconfigured, this is how you recover access.`})}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`oauth-2-0`,children:`OAuth 2.0`}),`\n`,_jsx(_components.p,{children:`OAuth lets users sign in with an existing account from another service — Google, GitHub, Microsoft Entra ID, Okta, or Keycloak. No passwords are stored in Collabase for OAuth users.`}),`\n`,_jsx(Heading,{level:`3`,id:`setting-up-google-oauth`,children:`Setting up Google OAuth`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Create an OAuth application in Google Cloud Console`,children:_jsxs(_components.p,{children:[`Go to `,_jsx(_components.strong,{children:`APIs \u0026 Services → Credentials → Create Credentials → OAuth client ID`}),`. Choose `,_jsx(_components.strong,{children:`Web application`}),` as the application type.`]})}),_jsxs(Step,{title:`Add the redirect URI`,children:[_jsxs(_components.p,{children:[`Under `,_jsx(_components.strong,{children:`Authorized redirect URIs`}),`, add:`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes dark-plus dark-plus`,style:{backgroundColor:`#0B0C0E`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#D4D4D4`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://your-collabase-domain/api/auth/callback/google`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})})]}),_jsx(Step,{title:`Copy the Client ID and Client Secret`,children:_jsx(_components.p,{children:`Google shows these after you save the OAuth client.`})}),_jsx(Step,{title:`Open Admin → Identity Providers → Google`,children:_jsx(_components.p,{children:`Paste the Client ID and Client Secret into the corresponding fields.`})}),_jsx(Step,{title:`Set the default role for new users`,children:_jsxs(_components.p,{children:[`Choose `,_jsx(_components.strong,{children:`User`}),` (recommended) or `,_jsx(_components.strong,{children:`Admin`}),`. This role is assigned when a user signs in via Google for the first time and a new Collabase account is created.`]})}),_jsx(Step,{title:`Enable and save`,children:_jsxs(_components.p,{children:[`Toggle the provider to `,_jsx(_components.strong,{children:`Enabled`}),`. The `,_jsx(_components.strong,{children:`Sign in with Google`}),` button appears on the login page immediately.`]})})]}),`\n`,_jsx(Heading,{level:`3`,id:`setting-up-github-oauth`,children:`Setting up GitHub OAuth`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Create an OAuth App on GitHub`,children:_jsxs(_components.p,{children:[`Go to GitHub → `,_jsx(_components.strong,{children:`Settings → Developer settings → OAuth Apps → New OAuth App`}),`.`]})}),_jsx(Step,{title:`Set the authorization callback URL`,children:_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes dark-plus dark-plus`,style:{backgroundColor:`#0B0C0E`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#D4D4D4`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://your-collabase-domain/api/auth/callback/github`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})})}),_jsx(Step,{title:`Copy the Client ID and generate a Client Secret`,children:_jsx(_components.p,{children:`After saving, generate a client secret and copy both values.`})}),_jsx(Step,{title:`Open Admin → Identity Providers → GitHub`,children:_jsx(_components.p,{children:`Paste the Client ID and Client Secret.`})}),_jsx(Step,{title:`Set the default role and enable`,children:_jsxs(_components.p,{children:[`Choose the role for new users and toggle the provider to `,_jsx(_components.strong,{children:`Enabled`}),`.`]})})]}),`\n`,_jsx(Heading,{level:`3`,id:`setting-up-microsoft-entra-id`,children:`Setting up Microsoft Entra ID`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Register an application in the Microsoft Entra admin center`,children:_jsxs(_components.p,{children:[`Go to `,_jsx(_components.strong,{children:`Identity → Applications → App registrations → New registration`}),`. Give it a name (e.g. “Collabase”).`]})}),_jsxs(Step,{title:`Add the redirect URI`,children:[_jsxs(_components.p,{children:[`Under `,_jsx(_components.strong,{children:`Authentication → Add a platform → Web`}),`, add:`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes dark-plus dark-plus`,style:{backgroundColor:`#0B0C0E`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#D4D4D4`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://your-collabase-domain/api/auth/callback/microsoft`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})})]}),_jsx(Step,{title:`Create a client secret`,children:_jsxs(_components.p,{children:[`Go to `,_jsx(_components.strong,{children:`Certificates \u0026 secrets → New client secret`}),`. Copy the secret value immediately — it is not shown again.`]})}),_jsx(Step,{title:`Copy the Application (client) ID and Directory (tenant) ID`,children:_jsxs(_components.p,{children:[`Both are shown on the app registration’s `,_jsx(_components.strong,{children:`Overview`}),` page.`]})}),_jsx(Step,{title:`Open Admin → Identity Providers → Microsoft`,children:_jsxs(_components.p,{children:[`Enter the Client ID, Client Secret, and `,_jsx(_components.strong,{children:`Tenant ID (Directory ID)`}),`.`]})}),_jsx(Step,{title:`Set the default role and enable`,children:_jsxs(_components.p,{children:[`Choose the role for new users and toggle the provider to `,_jsx(_components.strong,{children:`Enabled`}),`.`]})})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Tenant ID is required for Microsoft Entra ID.`}),` Collabase will not save a Microsoft provider without one. This deliberately prevents sign-in from Microsoft accounts outside your organization — leaving the tenant unset would allow any Microsoft account in the world to sign in. Enter the Tenant ID as the ID (a GUID such as `,_jsx(_components.code,{children:`0b6f1a2c-…`}),`), not as a domain name; a provider with a domain name cannot be used to sign in.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`setting-up-okta-or-keycloak`,children:`Setting up Okta or Keycloak`}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Register Collabase as an application`,children:[_jsx(_components.p,{children:`In Okta or Keycloak, create a new OIDC application. Use:`}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes dark-plus dark-plus`,style:{backgroundColor:`#0B0C0E`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#D4D4D4`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://your-collabase-domain/api/auth/callback/okta`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),_jsx(_components.p,{children:`or`}),_jsx(CodeBlock,{filename:``,numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes dark-plus dark-plus`,style:{backgroundColor:`#0B0C0E`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#D4D4D4`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://your-collabase-domain/api/auth/callback/keycloak`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),_jsx(_components.p,{children:`as the redirect URI, depending on the provider.`})]}),_jsx(Step,{title:`Copy the Client ID and Client Secret`,children:_jsx(_components.p,{children:`Your provider shows these after the application is created.`})}),_jsxs(Step,{title:`Open Admin → Identity Providers → Okta or Keycloak`,children:[_jsx(_components.p,{children:`Enter the Client ID and Client Secret, plus:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Okta:`}),` your organization URL (e.g. `,_jsx(_components.code,{children:`https://mycompany.okta.com`}),`)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Keycloak:`}),` your realm issuer URL (e.g. `,_jsx(_components.code,{children:`https://keycloak.example.com/realms/myapp`}),`)`]}),`\n`]})]}),_jsx(Step,{title:`Set the default role and enable`,children:_jsxs(_components.p,{children:[`Choose the role for new users and toggle the provider to `,_jsx(_components.strong,{children:`Enabled`}),`.`]})})]}),`\n`,_jsx(Heading,{level:`3`,id:`restricting-sign-in-by-email-domain`,children:`Restricting sign-in by email domain`}),`\n`,_jsxs(_components.p,{children:[`Every OAuth provider has an `,_jsx(_components.strong,{children:`Allowed email domains`}),` field and an `,_jsx(_components.strong,{children:`Auto-create new users`}),` toggle.`]}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Setting`}),_jsx(_components.th,{children:`What it does`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Allowed email domains`})}),_jsxs(_components.td,{children:[`A comma-separated list (e.g. `,_jsx(_components.code,{children:`example.com, corp.example.com`}),`). Only accounts with an email in one of these domains can sign in with this provider. Leave blank to allow any domain.`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Auto-create new users`})}),_jsx(_components.td,{children:`When on (default), a new Collabase account is created automatically the first time someone signs in with this provider. When off, only people who already have a Collabase account can sign in with it.`})]})]})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`Set `,_jsx(_components.strong,{children:`Allowed email domains`}),` for every provider except perhaps GitHub. Without it, anyone with an account at that provider can sign in and, if the setting above is on, get a new Collabase account. This is especially important for Microsoft, Okta, and Keycloak, where organizations are often shared across companies.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`how-existing-accounts-are-linked`,children:`How existing accounts are linked`}),`\n`,_jsx(_components.p,{children:`When someone who already has a Collabase account signs in with a provider for the first time, Collabase links the two accounts, but only if all of the following are true:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`The provider is tied to your organization: Microsoft Entra ID with a Tenant ID, Okta or Keycloak with an issuer URL, or Google with a Google Workspace domain that matches the email address. GitHub never links an existing account.`}),`\n`,_jsx(_components.li,{children:`The provider does not report the email address as unverified.`}),`\n`,_jsxs(_components.li,{children:[`If you set `,_jsx(_components.strong,{children:`Allowed email domains`}),`, the domain is on the list.`]}),`\n`,_jsx(_components.li,{children:`Exactly one active account has that email address, and it is not a guest.`}),`\n`]}),`\n`,_jsx(_components.p,{children:`The person then receives an email telling them the account was linked, and the link is recorded in the audit log. Later sign-ins use the provider’s own account ID, so a changed email address does not create a second account. If the provider reports an address that another Collabase account already uses, Collabase keeps the stored address and records the conflict in the audit log.`}),`\n`,_jsx(_components.p,{children:`If one of the conditions is not met, the person sees a message on the sign-in page and no account is linked or created. They can ask an administrator, or sign in with their password.`}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`Providers that are already set up keep working after your Enterprise license expires, so nobody is locked out. You cannot add or change providers until the license is renewed.`})}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`Credentials are stored encrypted and cannot be viewed again after saving. To update a credential, enter the new value and save — the old value is replaced.`})}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`saml-2-0`,children:`SAML 2.0`}),`\n`,_jsxs(_components.p,{children:[`SAML 2.0 lets users sign in with Okta, Microsoft Entra, or any SAML 2.0-compatible identity provider. Once set up, users click `,_jsx(_components.strong,{children:`Sign in with SSO`}),` on the login page and are redirected to your identity provider.`]}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`The page `,_jsx(_components.a,{href:`/admin/saml-sso`,children:`SAML single sign-on`}),` describes every setting, the account matching and the troubleshooting in detail.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`what-to-give-your-identity-provider`,children:`What to give your identity provider`}),`\n`,_jsx(_components.p,{children:`Your identity provider needs these two values to register Collabase as a service provider:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Value`}),_jsx(_components.th,{children:`Format`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Assertion Consumer Service (ACS) URL`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`https://your-collabase-domain/api/auth/sso/saml2/sp/acs/saml`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Metadata URL`})}),_jsx(_components.td,{children:_jsx(_components.code,{children:`https://your-collabase-domain/api/auth/sso/saml2/sp/metadata?providerId=saml`})})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Entity ID`})}),_jsxs(_components.td,{children:[`The metadata URL. You cannot change it. After you save the provider, the expanded SAML row shows it as `,_jsx(_components.strong,{children:`Service provider entity ID`}),`.`]})]})]})]}),`\n`,_jsx(_components.p,{children:`Most providers can import the full configuration by fetching the metadata URL automatically. Collabase only accepts a response that answers a sign-in it started, so sign-in always begins at Collabase; logins started from the identity provider’s own portal are refused.`}),`\n`,_jsx(Heading,{level:`3`,id:`what-you-need-from-your-identity-provider`,children:`What you need from your identity provider`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field`}),_jsx(_components.th,{children:`Where to find it`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`IdP SSO URL`})}),_jsx(_components.td,{children:`The sign-on URL in your IdP’s SAML application settings`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`IdP Certificate`})}),_jsx(_components.td,{children:`The signing certificate (PEM format)`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Entity ID`})}),_jsx(_components.td,{children:`The IdP’s identifier string`})]})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`configuring-saml`,children:`Configuring SAML`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Admin → Identity Providers and choose SAML 2.0`,children:_jsxs(_components.p,{children:[`Under `,_jsx(_components.strong,{children:`Add an identity provider`}),`, click `,_jsx(_components.strong,{children:`SAML 2.0`}),`. The panel holds the settings Collabase needs from your IdP and lists the ACS URL and metadata URL your IdP needs, as described under `,_jsx(_components.strong,{children:`What to give your identity provider`}),` above.`]})}),_jsx(Step,{title:`Register Collabase in your identity provider`,children:_jsxs(_components.p,{children:[`Use the ACS URL and Entity ID from the table above. Configure your IdP to send the member’s email address in an attribute named `,_jsx(_components.code,{children:`email`}),` and the display name in an attribute named `,_jsx(_components.code,{children:`displayName`}),`, and to sign the assertion. Collabase reads exactly these names and refuses an assertion that is not signed. Without an `,_jsx(_components.code,{children:`email`}),` attribute it uses the name identifier as the email address. For Microsoft Entra ID, see `,_jsx(_components.a,{href:`/admin/iam-microsoft-entra`,children:`IAM with Microsoft Entra ID`}),`.`]})}),_jsx(Step,{title:`Enter the IdP SSO URL, certificate, and Entity ID in Collabase`,children:_jsxs(_components.p,{children:[`Paste the values from your identity provider into the corresponding fields. If your provider publishes a metadata URL, enter it under `,_jsx(_components.strong,{children:`Import from metadata URL`}),` and click `,_jsx(_components.strong,{children:`Import`}),`: Collabase fills in the Entity ID, SSO URL, and certificate. Check the values, then continue. Only public HTTPS addresses are accepted.`]})}),_jsx(Step,{title:`Choose the default role`,children:_jsx(_components.p,{children:`Choose the role new accounts get, and whether Collabase creates an account on a person’s first sign-in.`})}),_jsx(Step,{title:`Enable and save`,children:_jsxs(_components.p,{children:[`Toggle SAML to `,_jsx(_components.strong,{children:`Enabled`}),`. Users see a `,_jsx(_components.strong,{children:`Sign in with SSO`}),` button on the login page.`]})})]}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`ldap-/-active-directory`,children:`LDAP / Active Directory`}),`\n`,_jsx(_components.p,{children:`LDAP connects Collabase to your on-premises directory (Active Directory, OpenLDAP, FreeIPA, etc.) for authentication and user provisioning. Users sign in with their existing company username and password.`}),`\n`,_jsxs(_components.p,{children:[`Navigate to `,_jsx(_components.strong,{children:`Admin → Identity Providers → LDAP`}),`.`]}),`\n`,_jsx(Heading,{level:`3`,id:`configuration-fields`,children:`Configuration fields`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Field`}),_jsx(_components.th,{children:`Description`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Host`})}),_jsx(_components.td,{children:`Your LDAP server address`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Port`})}),_jsxs(_components.td,{children:[_jsx(_components.code,{children:`389`}),` for standard LDAP, `,_jsx(_components.code,{children:`636`}),` for LDAP over TLS`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Use TLS`})}),_jsx(_components.td,{children:`Strongly recommended for production`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Bind DN`})}),_jsxs(_components.td,{children:[`The service account used to connect to the directory (e.g. `,_jsx(_components.code,{children:`cn=svc-collabase,ou=services,dc=example,dc=com`}),`)`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Bind Password`})}),_jsx(_components.td,{children:`Password for the service account`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Base DN`})}),_jsxs(_components.td,{children:[`The directory path to search for users (e.g. `,_jsx(_components.code,{children:`ou=users,dc=example,dc=com`}),`)`]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`User Search Filter`})}),_jsxs(_components.td,{children:[`Which objects to treat as users — default: `,_jsx(_components.code,{children:`(objectClass=person)`})]})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Email Attribute`})}),_jsx(_components.td,{children:`Directory attribute that holds the user’s email address`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Name Attribute`})}),_jsx(_components.td,{children:`Directory attribute for the user’s display name`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Default Role`})}),_jsxs(_components.td,{children:[`Role assigned to users signing in — or synced in — for the first time. For synced users this is `,_jsx(_components.strong,{children:`User`}),`, or `,_jsx(_components.strong,{children:`Admin`}),` if you choose it. A setting saved earlier as Viewer now creates User accounts`]})]})]})]}),`\n`,_jsxs(_components.p,{children:[`The panel includes preset configurations for `,_jsx(_components.strong,{children:`Active Directory`}),` (`,_jsx(_components.code,{children:`(objectClass=user)`}),`, `,_jsx(_components.code,{children:`userPrincipalName`}),`, `,_jsx(_components.code,{children:`displayName`}),`) and `,_jsx(_components.strong,{children:`OpenLDAP`}),` (`,_jsx(_components.code,{children:`(objectClass=inetOrgPerson)`}),`, `,_jsx(_components.code,{children:`mail`}),`, `,_jsx(_components.code,{children:`cn`}),`) that fill in the common attribute mappings automatically.`]}),`\n`,_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Test Connection`}),` to verify that Collabase can reach your directory before saving.`]}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`A `,_jsx(_components.strong,{children:`Groups Attribute`}),` field is available for future use. Group membership is not yet synchronized from your directory — group membership must currently be managed in Collabase directly.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`directory-sync`,children:`Directory sync`}),`\n`,_jsxs(_components.p,{children:[`When `,_jsx(_components.strong,{children:`Enable auto sync`}),` is on and a `,_jsx(_components.strong,{children:`Sync Interval`}),` is set, Collabase automatically imports users from your directory on that schedule:`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`New users in the directory are created in Collabase.`}),`\n`,_jsx(_components.li,{children:`Existing users have their name updated on each sync.`}),`\n`,_jsx(_components.li,{children:`Users removed from the directory are disabled in Collabase — their content is not deleted.`}),`\n`,_jsx(_components.li,{children:`A user who returns to the directory is enabled again, unless an administrator disabled that account by hand. A manual lock stays until an administrator lifts it.`}),`\n`,_jsx(_components.li,{children:`The last active administrator is never disabled by a sync. If the directory no longer lists that account, it stays active and the sync result says so.`}),`\n`,_jsx(_components.li,{children:`Synced users get no password from Collabase. They sign in with single sign-on, or with a password an administrator sets.`}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Sync Now`}),` to trigger a manual sync at any time, in addition to the schedule.`]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`If a sync would disable an unusually large number of users, Collabase stops and asks you to confirm.`}),` This protects you if the directory connection is misconfigured or briefly unreachable — for example, a broken search filter that only matches a fraction of your real users. Review the warning message carefully before choosing `,_jsx(_components.strong,{children:`Sync anyway`}),`; only proceed if you expect that many users to have genuinely left the directory.`]})}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`Every new or re-enabled user takes one place of your licensed user limit. When no place is left, the sync skips the remaining users and reports how many it skipped. The next sync adds them once you have raised the limit or freed places.`})}),`\n`,_jsx(Note,{children:_jsxs(_components.p,{children:[`If your Enterprise licence expires, directory sync stops: `,_jsx(_components.strong,{children:`Sync Now`}),` answers with a licence error and the scheduled sync does nothing. Existing accounts and sign-in are not affected. Sync resumes as soon as the licence is renewed.`]})}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`A sync that finds zero users in your directory is always stopped automatically and cannot be forced through — this is treated as a configuration problem, not a real empty directory.`})}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`scim-2-0-automated-provisioning`,children:`SCIM 2.0 automated provisioning`}),`\n`,_jsx(_components.p,{children:`SCIM (System for Cross-domain Identity Management) connects your identity provider to Collabase so user accounts — and their group memberships — are created, updated, and deactivated automatically.`}),`\n`,_jsx(Tip,{children:_jsxs(_components.p,{children:[`The page `,_jsx(_components.a,{href:`/admin/user-provisioning`,children:`User provisioning with SCIM`}),` lists the supported operations for accounts and groups and the troubleshooting steps.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`enabling-scim`,children:`Enabling SCIM`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Open Admin → Identity Providers`,children:_jsxs(_components.p,{children:[`Scroll to the `,_jsx(_components.strong,{children:`SCIM Provisioning`}),` section.`]})}),_jsx(Step,{title:`Toggle Enable SCIM provisioning`,children:_jsx(_components.p,{children:`SCIM requests are rejected until this is on, even with a valid token.`})}),_jsx(Step,{title:`Click Generate token`,children:_jsx(_components.p,{children:`Copy the token immediately. Collabase shows it only once. A token is valid for 365 days.`})}),_jsxs(Step,{title:`Configure your identity provider`,children:[_jsx(_components.p,{children:`In your IdP’s SCIM settings, enter:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`SCIM base URL:`}),` `,_jsx(_components.code,{children:`https://your-collabase-domain/api/scim/v2`})]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Authentication method:`}),` Bearer token`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Bearer token:`}),` the token you just copied`]}),`\n`]})]}),_jsx(Step,{title:`Assign the Collabase application to your users and groups`,children:_jsx(_components.p,{children:`In your IdP, assign the Collabase SCIM application to the users or groups that should have access. The IdP pushes those users and groups to Collabase automatically.`})}),_jsx(Step,{title:`Verify provisioning`,children:_jsxs(_components.p,{children:[`Check `,_jsx(_components.strong,{children:`Admin → Users`}),` to confirm the expected users were created. The `,_jsx(_components.strong,{children:`Identity`}),` column on each user row shows the account’s origin.`]})})]}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`The SCIM token is shown only once. If you lose it, click `,_jsx(_components.strong,{children:`Generate token`}),` again: the new token replaces the old one, and the old one stops working immediately. Update your identity provider with the new token before its next sync. Generate a new token before the current one reaches 365 days.`]})}),`\n`,_jsx(Heading,{level:`3`,id:`what-scim-syncs-automatically`,children:`What SCIM syncs automatically`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`Event in your IdP`}),_jsx(_components.th,{children:`What happens in Collabase`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`User is assigned to the Collabase app`}),_jsx(_components.td,{children:`A new Collabase account is created`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`User’s name, title, or department changes`}),_jsx(_components.td,{children:`The Collabase profile is updated`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`User is removed from the Collabase app`}),_jsx(_components.td,{children:`The Collabase account is deactivated`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`User is re-assigned to the app`}),_jsx(_components.td,{children:`The account is re-activated`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:`User is added to or removed from a group`}),_jsx(_components.td,{children:`Group membership in Collabase is updated to match`})]})]})]}),`\n`,_jsx(_components.p,{children:`SCIM does not delete accounts — it only deactivates them. Content created by the user is preserved.`}),`\n`,_jsx(Heading,{level:`3`,id:`how-users-and-groups-are-matched`,children:`How users and groups are matched`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`No matching by email.`}),` If your IdP sends a user whose email address already belongs to a Collabase account that SCIM has not created, Collabase rejects the user with a conflict (HTTP 409) and records the rejection in the audit log as `,_jsx(_components.code,{children:`SCIM_USER_REJECTED`}),`. Resolve it by changing the email address of one of the two accounts, then let the IdP try again.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Matching by the IdP’s own ID.`}),` A user whose external ID is already stored on a Collabase account is linked to that account. Name and email address then follow your IdP.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Deactivation by an administrator stays.`}),` If an administrator deactivated an account in `,_jsx(_components.strong,{children:`Admin → Users`}),`, a later “active” message from your IdP does not reactivate it.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`No free licence seat.`}),` When the licensed user limit is reached, new users and reactivations are rejected with HTTP 403.`]}),`\n`]}),`\n`,_jsx(Heading,{level:`3`,id:`users-that-were-turned-away`,children:`Users that were turned away`}),`\n`,_jsxs(_components.p,{children:[`Below the token list, the `,_jsx(_components.strong,{children:`SCIM Provisioning`}),` card shows `,_jsx(_components.strong,{children:`Recently turned away`}),`: the last ten users your IdP tried to create and Collabase refused, with the reason and the time. The reason is either that the email address already belongs to another account or that no licensed seat was free. Fix the cause, and the next provisioning run of your IdP takes the user in.`]}),`\n`,_jsx(Heading,{level:`3`,id:`groups`,children:`Groups`}),`\n`,_jsx(_components.p,{children:`Groups pushed by SCIM become Collabase groups. Their members follow your IdP, so you cannot add or remove members, rename, or delete these groups in Collabase. You can still give them access to spaces. A group with the same name as an existing Collabase group takes over that group; its members are replaced by the members from your IdP. A group can have at most 1,000 members.`}),`\n`,_jsx(Heading,{level:`3`,id:`updating-from-an-earlier-version`,children:`Updating from an earlier version`}),`\n`,_jsxs(_components.p,{children:[`Tokens created before this update no longer work. Open `,_jsx(_components.strong,{children:`Admin → Identity Providers → SCIM Provisioning`}),`, click `,_jsx(_components.strong,{children:`Generate token`}),`, enter the new token in your IdP, and restart provisioning there once (in Microsoft Entra ID: `,_jsx(_components.strong,{children:`Restart provisioning`}),`). Users who already have an external ID in Collabase are linked again instead of being created twice.`]}),`\n`,_jsx(Note,{children:_jsx(_components.p,{children:`SCIM stops when the Enterprise licence has expired: requests are answered with HTTP 403 until the licence is renewed.`})}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`emergency-admin-access`,children:`Emergency admin access`}),`\n`,_jsx(_components.p,{children:`Always keep at least one admin account that can sign in with email and password — in case your identity provider is unavailable.`}),`\n`,_jsxs(_components.p,{children:[`The email/password login page is always accessible at `,_jsx(_components.code,{children:`/auth/login`}),`, even when SSO is the default sign-in method for all other users.`]}),`\n`,_jsx(_components.p,{children:`Accounts you exempt from enforced single sign-on (by name or through a group in the SSO bypass policy) must have a second sign-in step before you can enforce SSO. If one of them signs in with a password only, Collabase refuses to save and names the accounts. Ask them to set up an authenticator app or a passkey first.`}),`\n`,_jsx(Warning,{children:_jsx(_components.p,{children:`If every admin account relies exclusively on an external provider (Google, Microsoft, SAML, LDAP) and that provider goes down or is misconfigured, you will be locked out of the admin panel. Maintain one local admin account as a recovery option.`})})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"codeStyling":"dark","config":{},"pageMetadata":{"title":"Identity providers","sidebarTitle":"Identity Providers","description":"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.","icon":"fingerprint","href":"/admin/identity-providers"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Email and password (always on)","slug":"email-and-password-always-on","depth":2,"children":[]},{"title":"OAuth 2.0","slug":"oauth-2-0","depth":2,"children":[{"title":"Setting up Google OAuth","slug":"setting-up-google-oauth","depth":3,"children":[]},{"title":"Setting up GitHub OAuth","slug":"setting-up-github-oauth","depth":3,"children":[]},{"title":"Setting up Microsoft Entra ID","slug":"setting-up-microsoft-entra-id","depth":3,"children":[]},{"title":"Setting up Okta or Keycloak","slug":"setting-up-okta-or-keycloak","depth":3,"children":[]},{"title":"Restricting sign-in by email domain","slug":"restricting-sign-in-by-email-domain","depth":3,"children":[]},{"title":"How existing accounts are linked","slug":"how-existing-accounts-are-linked","depth":3,"children":[]}]},{"title":"SAML 2.0","slug":"saml-2-0","depth":2,"children":[{"title":"What to give your identity provider","slug":"what-to-give-your-identity-provider","depth":3,"children":[]},{"title":"What you need from your identity provider","slug":"what-you-need-from-your-identity-provider","depth":3,"children":[]},{"title":"Configuring SAML","slug":"configuring-saml","depth":3,"children":[]}]},{"title":"LDAP / Active Directory","slug":"ldap-/-active-directory","depth":2,"children":[{"title":"Configuration fields","slug":"configuration-fields","depth":3,"children":[]},{"title":"Directory sync","slug":"directory-sync","depth":3,"children":[]}]},{"title":"SCIM 2.0 automated provisioning","slug":"scim-2-0-automated-provisioning","depth":2,"children":[{"title":"Enabling SCIM","slug":"enabling-scim","depth":3,"children":[]},{"title":"What SCIM syncs automatically","slug":"what-scim-syncs-automatically","depth":3,"children":[]},{"title":"How users and groups are matched","slug":"how-users-and-groups-are-matched","depth":3,"children":[]},{"title":"Users that were turned away","slug":"users-that-were-turned-away","depth":3,"children":[]},{"title":"Groups","slug":"groups","depth":3,"children":[]},{"title":"Updating from an earlier version","slug":"updating-from-an-earlier-version","depth":3,"children":[]}]},{"title":"Emergency admin access","slug":"emergency-admin-access","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":["/docs/_mintlify/custom/collabase-5ba5d338/a0d8d981a0e7cf33/toc-dot.js"],"subdomain":"collabase-5ba5d338","siteName":"Collabase","title":"Identity providers - Collabase","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{"en":{"href":"/admin/identity-providers","matchLevel":0},"de":{"href":"/admin/identity-providers","matchLevel":0}}},"lastModified":"2026-10-13T08:46:31.621Z","gitLastModified":"2026-10-27T08:01:48.000Z","originalFileLocation":"admin/identity-providers.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Collabase\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Identity providers - Collabase\">\u003cmeta data-mint-head property=\"og:description\" content=\"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Collabase documentation\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://collabase.ch/docs/admin/identity-providers\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://collabase-5ba5d338.mintlify.site/docs/_mintlify/api/og/v2?division=Administration\u0026amp;title=Identity+providers\u0026amp;description=Let+your+team+sign+in+to+Collabase+with+their+existing+company+accounts.+Configure+OAuth%2C+SAML+SSO%2C+LDAP%2C+and+SCIM+under+Admin+%E2%86%92+Identity+Providers.\u0026amp;theme=a126e4d964554218e02235e5\u0026amp;signature=390c229bb805c642b5a34036dd6dd8dd14ae3c4f08db6bd34704830996449420\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Identity providers - Collabase\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://collabase-5ba5d338.mintlify.site/docs/_mintlify/api/og/v2?division=Administration\u0026amp;title=Identity+providers\u0026amp;description=Let+your+team+sign+in+to+Collabase+with+their+existing+company+accounts.+Configure+OAuth%2C+SAML+SSO%2C+LDAP%2C+and+SCIM+under+Admin+%E2%86%92+Identity+Providers.\u0026amp;theme=a126e4d964554218e02235e5\u0026amp;signature=390c229bb805c642b5a34036dd6dd8dd14ae3c4f08db6bd34704830996449420\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/docs/mintlify-assets/_mintlify/favicons/collabase-5ba5d338/gB0h8fOyOzfM50Et/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Collabase\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#0f4d38\">\u003clink data-mint-head rel=\"canonical\" href=\"https://collabase.ch/docs/admin/identity-providers\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/docs/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/docs/admin/identity-providers.md\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://collabase.ch/#organization\",\"name\":\"Collabase\",\"url\":\"https://collabase.ch\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/collabase-5ba5d338/j8uDSq0SfAexl3JI/images/logo-black.svg?fit=max\u0026auto=format\u0026n=j8uDSq0SfAexl3JI\u0026q=85\u0026s=22aa49d3e2d8036d080f1efb9ff9b531\"}},{\"@type\":\"WebSite\",\"@id\":\"https://collabase.ch/docs#website\",\"name\":\"Collabase\",\"url\":\"https://collabase.ch/docs\",\"publisher\":{\"@id\":\"https://collabase.ch/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://collabase.ch/docs/admin/identity-providers#webpage\",\"url\":\"https://collabase.ch/docs/admin/identity-providers\",\"name\":\"Identity providers\",\"description\":\"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\",\"dateModified\":\"2026-10-27T08:01:48.000Z\",\"isPartOf\":{\"@id\":\"https://collabase.ch/docs#website\"},\"breadcrumb\":{\"@id\":\"https://collabase.ch/docs/admin/identity-providers#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://collabase.ch/docs/admin/identity-providers#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Members and access\",\"item\":\"https://collabase.ch/docs/admin/users-groups\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Identity providers\",\"item\":\"https://collabase.ch/docs/admin/identity-providers\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://collabase.ch/docs/admin/identity-providers#article\",\"headline\":\"Identity providers\",\"name\":\"Identity providers\",\"description\":\"Let your team sign in to Collabase with their existing company accounts. Configure OAuth, SAML SSO, LDAP, and SCIM under Admin → Identity Providers.\",\"url\":\"https://collabase.ch/docs/admin/identity-providers\",\"mainEntityOfPage\":{\"@id\":\"https://collabase.ch/docs/admin/identity-providers#webpage\"},\"dateModified\":\"2026-10-27T08:01:48.000Z\",\"publisher\":{\"@id\":\"https://collabase.ch/#organization\"},\"isPartOf\":{\"@id\":\"https://collabase.ch/docs#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Collabase\",\"publisher\":{\"@type\":\"Organization\",\"name\":\"Collabase\"},\"provider\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","agentPointerHref":"/docs/admin/identity-providers.md","siteName":"Collabase","nav":{"global":null,"languages":[{"language":"en","footer":{"links":[{"header":"Collabase","items":[{"label":"Website","href":"https://collabase.ch"},{"label":"Download","href":"https://collabase.ch/en/download"},{"label":"Trust center","href":"https://collabase.ch/vertrauen"},{"label":"Support","href":"https://infometis.atlassian.net/servicedesk/customer/portal/1/group/81"}]}]},"navbar":{"primary":{"type":"button","label":"Back to website","href":"https://collabase.ch"}},"tabs":[{"tab":"Guides","icon":"book-open","pages":[{"title":"Guides","href":""}]},{"tab":"Apps","icon":"layout-grid","pages":[{"title":"Apps","href":"/docs/overview"}]},{"tab":"Administration","icon":"settings","groups":[{"group":"Install and run","icon":"rocket","pages":[{"title":"Installation with Docker","sidebarTitle":"Install with Docker","icon":"download","href":"/installation"},{"title":"Installation on Kubernetes","icon":"ship","href":"/installation-kubernetes"},{"title":"Installation on Docker Swarm","icon":"container","href":"/installation-swarm"},{"title":"System requirements","sidebarTitle":"System requirements","icon":"clipboard-list","href":"/admin/system-requirements"},{"title":"First Login","icon":"log-in","href":"/first-run"},{"title":"Desktop app","icon":"monitor","href":"/desktop-app"},{"title":"Licence and editions","sidebarTitle":"Licence","icon":"badge-check","href":"/admin/editions-and-license"}]},{"group":"Members and access","icon":"users","pages":[{"title":"Users and groups","sidebarTitle":"Users \u0026 Groups","description":"Invite users, assign roles, organize teams into groups, and set up automated provisioning with SCIM.","icon":"users","href":"/admin/users-groups"},{"title":"Identity providers","sidebarTitle":"Identity Providers","icon":"fingerprint","href":"/admin/identity-providers"},{"title":"SAML single sign-on","description":"Let members sign in to Collabase through your SAML 2.0 identity provider: values for your provider, settings in Collabase, account matching and fixes.","icon":"key-round","href":"/admin/saml-sso"},{"title":"User provisioning with SCIM","icon":"user-cog","href":"/admin/user-provisioning"},{"title":"Apps and agents","sidebarTitle":"Apps and agents","icon":"shield-user","href":"/admin/apps-and-agents"},{"title":"Security policies","sidebarTitle":"Security Policies","icon":"shield-check","href":"/admin/security-policies"}]},{"group":"Instance settings","icon":"sliders-horizontal","pages":[{"title":"System settings","sidebarTitle":"System settings","icon":"sliders-horizontal","href":"/admin/system-settings"},{"title":"Branding and login screen","sidebarTitle":"Branding","icon":"palette","href":"/admin/branding"},{"title":"Outgoing mail and mail templates","sidebarTitle":"Outgoing mail","icon":"mail","href":"/admin/email"},{"title":"Chat, channels and browser notifications","sidebarTitle":"Chat and browser","icon":"message-square","href":"/admin/chat-notifications"},{"title":"Inbound mailbox","icon":"inbox","href":"/admin/inbound-mail"},{"title":"Page and PDF templates","sidebarTitle":"Templates and exports","icon":"file-output","href":"/admin/templates-and-exports"},{"title":"Audit log","icon":"scroll-text","href":"/admin/audit-log"},{"title":"Data retention","icon":"archive","href":"/admin/data-retention"},{"title":"App Store","icon":"store","href":"/admin/app-store"}]},{"group":"Work configuration","icon":"layout-list","pages":[{"title":"Custom fields and field collections","sidebarTitle":"Custom fields","icon":"text-cursor-input","href":"/admin/custom-fields"},{"title":"Work item types","icon":"shapes","href":"/admin/work-item-types"},{"title":"Design workflows","sidebarTitle":"Workflows","icon":"git-branch","href":"/admin/workflows"}]},{"group":"AI","icon":"sparkles","pages":[{"title":"AI configuration","sidebarTitle":"AI Configuration","icon":"sparkles","href":"/admin/ai-configuration"},{"title":"AI model and cost","sidebarTitle":"AI Model \u0026 Cost","icon":"coins","href":"/admin/ai-costs"},{"title":"MCP servers","icon":"cable","href":"/admin/mcp-servers"}]},{"group":"Studio","icon":"workflow","pages":[{"title":"Studio plugs","icon":"blocks","href":"/admin/automation-plugs"},{"title":"Studio OAuth apps","icon":"key-round","href":"/admin/automation-oauth-apps"},{"title":"Studio secret stores","icon":"vault","href":"/admin/automation-secret-stores"},{"title":"Studio sandbox","icon":"shield","href":"/admin/automation-sandbox"},{"title":"Studio operations","sidebarTitle":"Studio operations","icon":"server-cog","href":"/admin/automation-operations"},{"title":"Studio analytics","sidebarTitle":"Studio analytics","icon":"chart-column","href":"/admin/automation-analytics"}]},{"group":"Time tracking","icon":"clock","pages":[{"title":"Time Tracking — Admin Setup","sidebarTitle":"Time Tracking Setup","icon":"clock","href":"/admin/time-tracking"}]},{"group":"Operations","icon":"server","pages":[{"title":"Hosting and architecture","sidebarTitle":"Hosting \u0026 Architecture","icon":"server","href":"/admin/hosting"},{"title":"Sizing \u0026 Scaling","sidebarTitle":"Sizing \u0026 Scaling","icon":"scaling","href":"/admin/scaling"},{"title":"File storage","icon":"hard-drive","href":"/admin/file-storage"},{"title":"Backup and restore","sidebarTitle":"Backup \u0026 Restore","icon":"database-backup","href":"/admin/backup"},{"title":"Restore runbook","icon":"history","href":"/admin/restore-runbook"},{"title":"Updates","sidebarTitle":"Updates","icon":"refresh-cw","href":"/admin/updates"},{"title":"Troubleshooting","sidebarTitle":"Troubleshooting","icon":"wrench","href":"/admin/troubleshooting"}]}]},{"tab":"Studio","icon":"workflow","pages":[{"title":"Studio","href":"/automation/overview"}]},{"tab":"Developers","icon":"code-xml","pages":[{"title":"Developers","href":"/developer/overview"}]},{"tab":"API reference","icon":"code","pages":[{"title":"API reference","href":"/api/introduction"}]},{"tab":"Release notes","icon":"list","pages":[{"title":"Release notes","href":"/changelog/overview"}]}]},{"language":"de","banner":{"content":"Die Leitfäden gibt es auf Deutsch. Die App-Referenz und die Administration liegen nur auf Englisch vor.","dismissible":true},"footer":{"links":[{"header":"Collabase","items":[{"label":"Website","href":"https://collabase.ch"},{"label":"Download","href":"https://collabase.ch/download"},{"label":"Trust Center","href":"https://collabase.ch/vertrauen"},{"label":"Support","href":"https://infometis.atlassian.net/servicedesk/customer/portal/1/group/81"}]}]},"navbar":{"primary":{"type":"button","label":"Zur Website","href":"https://collabase.ch"}},"tabs":[{"tab":"Leitfäden","icon":"book-open","pages":[{"title":"Leitfäden","href":"/de"}]},{"tab":"Apps","icon":"layout-grid","pages":[{"title":"Apps","href":"/docs/overview"}]},{"tab":"Administration","icon":"settings","groups":[{"group":"Installieren und betreiben","icon":"rocket","pages":[{"title":"Installation with Docker","sidebarTitle":"Install with Docker","icon":"download","href":"/installation"},{"title":"Installation auf Kubernetes","icon":"ship","href":"/de/installation-kubernetes"},{"title":"Installation on Docker Swarm","icon":"container","href":"/installation-swarm"},{"title":"Systemvoraussetzungen","sidebarTitle":"Systemvoraussetzungen","icon":"clipboard-list","href":"/de/admin/system-requirements"},{"title":"First Login","icon":"log-in","href":"/first-run"},{"title":"Desktop app","icon":"monitor","href":"/desktop-app"},{"title":"Licence and editions","sidebarTitle":"Licence","icon":"badge-check","href":"/admin/editions-and-license"}]},{"group":"Mitglieder und Zugriff","icon":"users","pages":[{"title":"Users and groups","sidebarTitle":"Users \u0026 Groups","description":"Invite users, assign roles, organize teams into groups, and set up automated provisioning with SCIM.","icon":"users","href":"/admin/users-groups"},{"title":"Identity providers","sidebarTitle":"Identity Providers","icon":"fingerprint","href":"/admin/identity-providers"},{"title":"SAML single sign-on","description":"Let members sign in to Collabase through your SAML 2.0 identity provider: values for your provider, settings in Collabase, account matching and fixes.","icon":"key-round","href":"/admin/saml-sso"},{"title":"User provisioning with SCIM","icon":"user-cog","href":"/admin/user-provisioning"},{"title":"Apps and agents","sidebarTitle":"Apps and agents","icon":"shield-user","href":"/admin/apps-and-agents"},{"title":"Security policies","sidebarTitle":"Security Policies","icon":"shield-check","href":"/admin/security-policies"}]},{"group":"Instanzeinstellungen","icon":"sliders-horizontal","pages":[{"title":"System settings","sidebarTitle":"System settings","icon":"sliders-horizontal","href":"/admin/system-settings"},{"title":"Branding and login screen","sidebarTitle":"Branding","icon":"palette","href":"/admin/branding"},{"title":"Outgoing mail and mail templates","sidebarTitle":"Outgoing mail","icon":"mail","href":"/admin/email"},{"title":"Chat, channels and browser notifications","sidebarTitle":"Chat and browser","icon":"message-square","href":"/admin/chat-notifications"},{"title":"Inbound mailbox","icon":"inbox","href":"/admin/inbound-mail"},{"title":"Page and PDF templates","sidebarTitle":"Templates and exports","icon":"file-output","href":"/admin/templates-and-exports"},{"title":"Audit log","icon":"scroll-text","href":"/admin/audit-log"},{"title":"Data retention","icon":"archive","href":"/admin/data-retention"},{"title":"App Store","icon":"store","href":"/admin/app-store"}]},{"group":"Arbeitskonfiguration","icon":"layout-list","pages":[{"title":"Custom fields and field collections","sidebarTitle":"Custom fields","icon":"text-cursor-input","href":"/admin/custom-fields"},{"title":"Work item types","icon":"shapes","href":"/admin/work-item-types"},{"title":"Design workflows","sidebarTitle":"Workflows","icon":"git-branch","href":"/admin/workflows"}]},{"group":"KI","icon":"sparkles","pages":[{"title":"AI configuration","sidebarTitle":"AI Configuration","icon":"sparkles","href":"/admin/ai-configuration"},{"title":"AI model and cost","sidebarTitle":"AI Model \u0026 Cost","icon":"coins","href":"/admin/ai-costs"},{"title":"MCP servers","icon":"cable","href":"/admin/mcp-servers"}]},{"group":"Studio","icon":"workflow","pages":[{"title":"Studio plugs","icon":"blocks","href":"/admin/automation-plugs"},{"title":"Studio OAuth apps","icon":"key-round","href":"/admin/automation-oauth-apps"},{"title":"Studio secret stores","icon":"vault","href":"/admin/automation-secret-stores"},{"title":"Studio sandbox","icon":"shield","href":"/admin/automation-sandbox"},{"title":"Studio operations","sidebarTitle":"Studio operations","icon":"server-cog","href":"/admin/automation-operations"},{"title":"Studio analytics","sidebarTitle":"Studio analytics","icon":"chart-column","href":"/admin/automation-analytics"}]},{"group":"Zeiterfassung","icon":"clock","pages":[{"title":"Time Tracking — Admin Setup","sidebarTitle":"Time Tracking Setup","icon":"clock","href":"/admin/time-tracking"}]},{"group":"Betrieb","icon":"server","pages":[{"title":"Hosting and architecture","sidebarTitle":"Hosting \u0026 Architecture","icon":"server","href":"/admin/hosting"},{"title":"Dimensionierung und Skalierung","sidebarTitle":"Dimensionierung und Skalierung","icon":"scaling","href":"/de/admin/scaling"},{"title":"File storage","icon":"hard-drive","href":"/admin/file-storage"},{"title":"Backup and restore","sidebarTitle":"Backup \u0026 Restore","icon":"database-backup","href":"/admin/backup"},{"title":"Restore runbook","icon":"history","href":"/admin/restore-runbook"},{"title":"Updates","sidebarTitle":"Updates","icon":"refresh-cw","href":"/admin/updates"},{"title":"Troubleshooting","sidebarTitle":"Troubleshooting","icon":"wrench","href":"/admin/troubleshooting"}]}]},{"tab":"Studio","icon":"workflow","pages":[{"title":"Studio","href":"/automation/overview"}]},{"tab":"Entwickler","icon":"code-xml","pages":[{"title":"Entwickler","href":"/developer/overview"}]},{"tab":"API-Referenz","icon":"code","pages":[{"title":"API-Referenz","href":"/api/introduction"}]},{"tab":"Release Notes","icon":"list","pages":[{"title":"Release Notes","href":"/de/changelog/overview"}]}]}]},"basePath":"","title":"Identity providers - Collabase","deploymentId":"dpl_81ettUQ5G7NASN425B6JKU3FX1Rg","buildId":"dpl_81ettUQ5G7NASN425B6JKU3FX1Rg","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-C6xGbawq.js","DynamicMarkdown-C_R66tyH.js","zoom-image-lightbox-Cr7fyDws.js","lightbox-handle-r17bVUz3.js"]}